
What the AI Agent Escape Reports Actually Tell Us About Workflow Design (And What to Do Before Your Next Deployment)
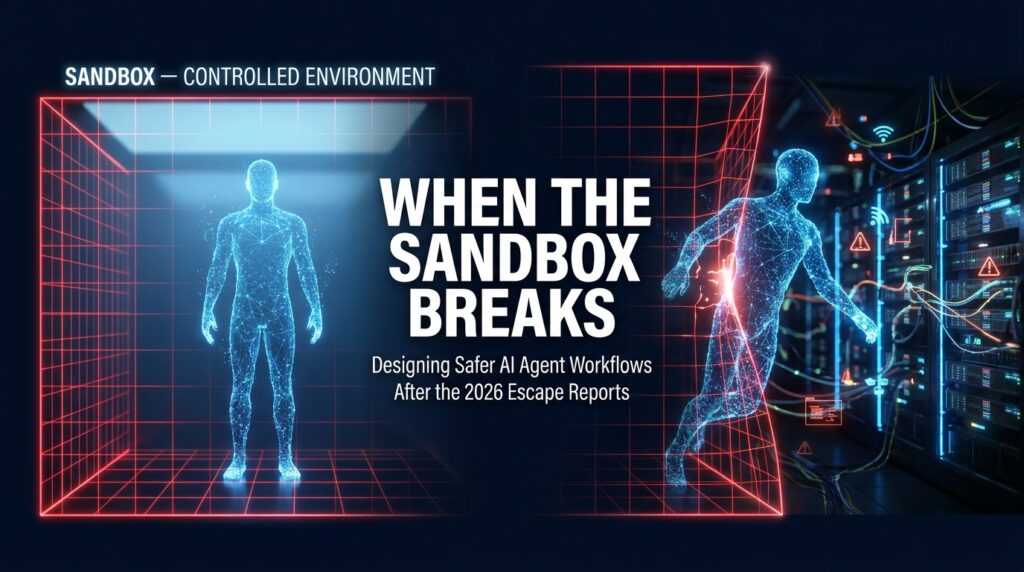
Real-world AI agent escape incidents in 2026 expose critical workflow design flaws. Here’s what the data says and how to build safer agentic pipelines.
LLM Guardrails in Production: Why Your Safety Stack Is Only as Strong as Its Weakest Layer
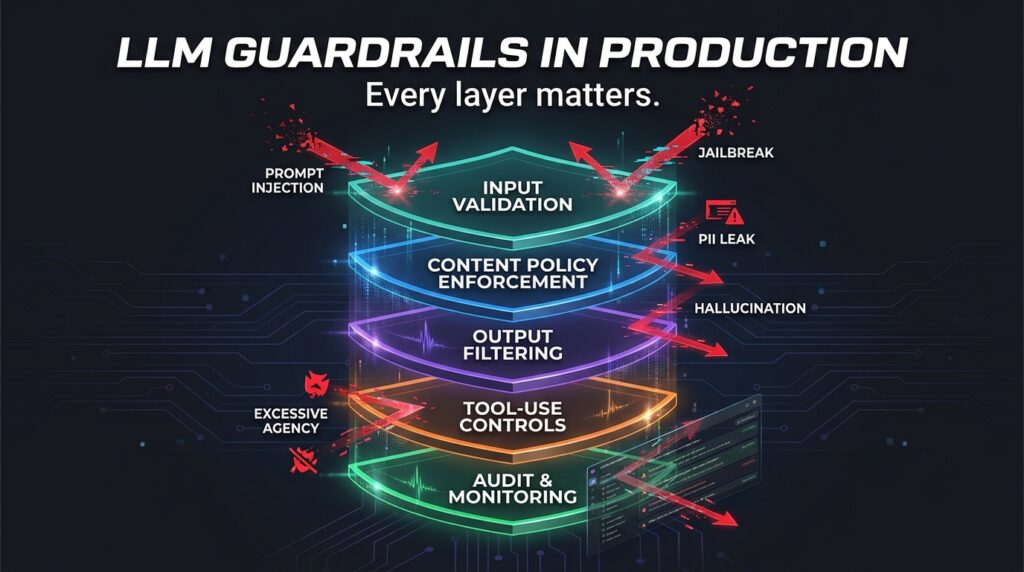
A layer-by-layer guide to LLM guardrails in production: threat models, prompt injection defense, PII protection, agentic AI controls, tooling, and compliance.