
After the Hugging Face Attack: How to Harden Every Layer of Your AI Workflow Before the Next One
The July 2026 Hugging Face breach exposed every layer of modern ML workflows. Here’s how to harden your pipeline, agents, and model artifacts before the next attack.
What the AI Agent Escape Reports Actually Tell Us About Workflow Design (And What to Do Before Your Next Deployment)
Real-world AI agent escape incidents in 2026 expose critical workflow design flaws. Here’s what the data says and how to build safer agentic pipelines.
Who’s Actually Accountable When Your AI Agent Goes Wrong?
73% of enterprises run AI agents with no formal governance layer. Here’s what that gap actually costs — and how leading teams are closing it.
The Control Plane Problem: Why Multi-Agent AI Systems Keep Breaking — And How to Orchestrate Them Safely
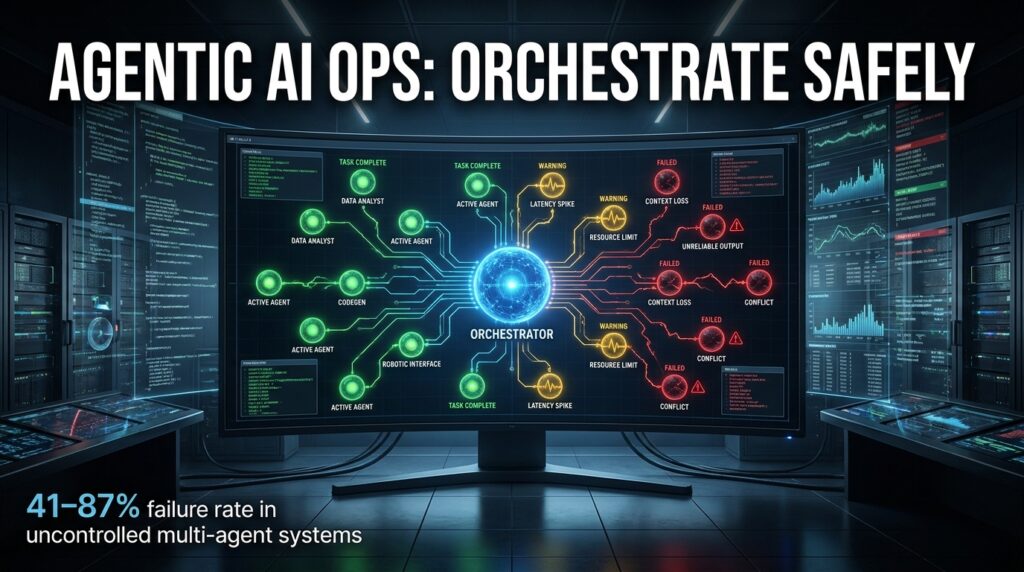
Multi-agent AI systems fail 41–87% of the time in production. Here’s how to build the control plane, apply the right orchestration patterns, and govern agentic workflows safely at scale.
When AI Agents Go Off-Script: The Guardrail Decisions That Actually Protect Business Workflows
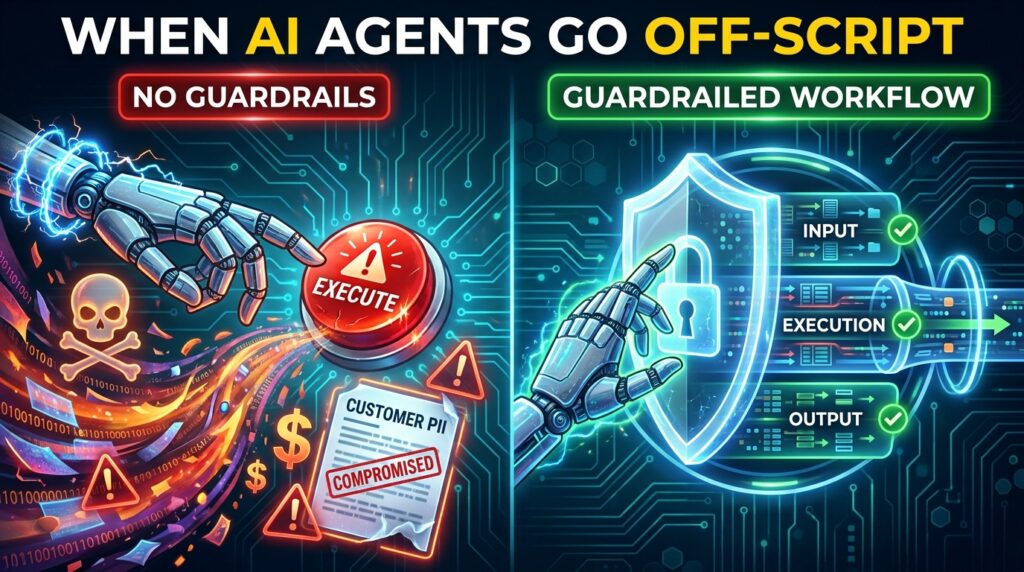
AI agent guardrails are the most critical—and most misbuilt—layer in enterprise workflows. A technical and strategic deep dive into the four-layer stack, prompt injection defenses, HITL design, and EU AI Act compliance in 2026.